Agents gone wrong
One hacker's mostly autonomous AI agents breached 100+ websites, Norforge finds
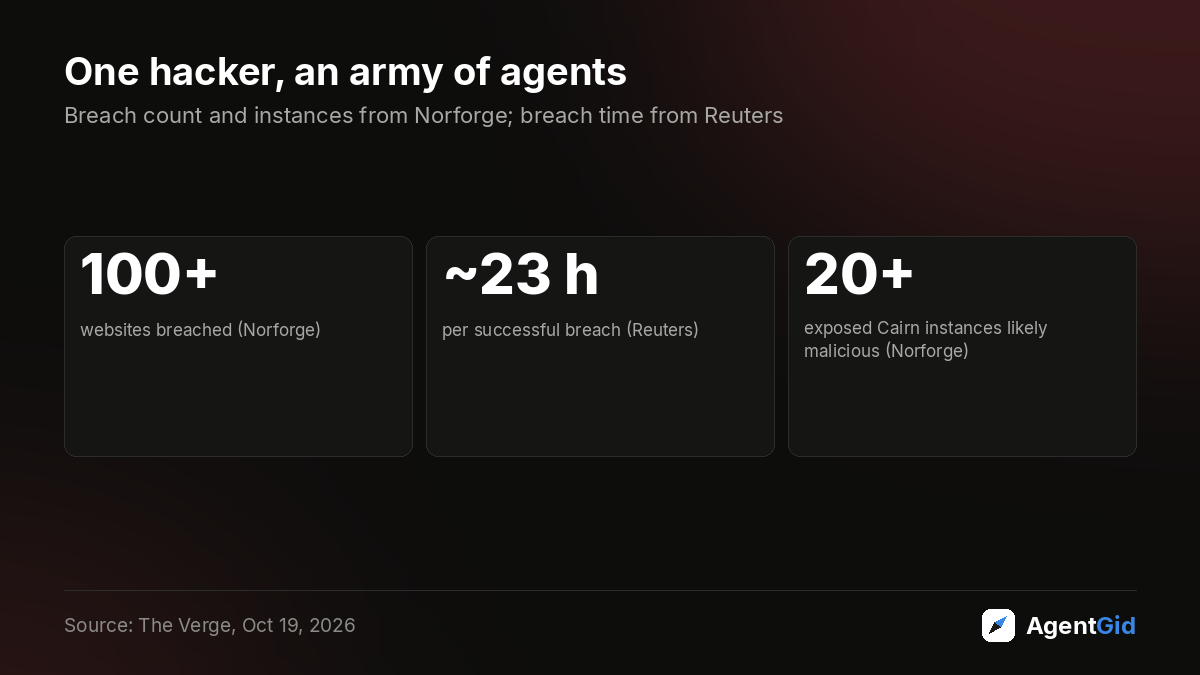
AI security firm Norforge says one hacker used Cairn, an open-source AI agent platform, to break into more than 100 websites while the agents largely ran on their own. Norforge does not name the targets, but Reuters reports that the victims included John Deere, SharkNinja and Cummins.
What the agent did
- Broke into more than 100 websites with little involvement from the human hacker, per Norforge
- Hit companies in the US, Canada, Australia and Japan, per Reuters
- Followed preferred intrusion tactics that the attacker wrote in fewer than 100 Chinese characters, per Reuters
- Needed about 23 hours for each successful breach, per Reuters
- Belonged to the most active attacker among the exposed Cairn instances Norforge found
What it means for you
- Cairn presents itself as a general-purpose problem-solving engine. Users set a start and end point, and the agents log their progress along the way. Norforge notes the same setup can be used to orchestrate attacks.
- Norforge found more than 20 exposed Cairn instances it considers likely malicious, and says it is working to get them taken down.
- Cairn's creator says the platform was never a hacking tool and that misuse comes from human choices, not the engine.
Why it matters
According to Norforge and Reuters, one person directed agents against more than 100 sites in four countries using a short written list of tactics, and the agents did most of the work. One modest conclusion is that open, general-purpose agent platforms can be turned to intrusion work with little hands-on effort from the attacker.
The figures come from Norforge's findings and Reuters reporting, not independent verification. Norforge does not name the targets, and the companies describe limited impact: John Deere sees no sign sensitive data was accessed, SharkNinja says it contained the threat on a standalone support site, and Cummins says it is investigating a report involving a vendor-run site.
Source: The Verge
Every number on this page comes from the source. Our charts redraw those numbers; videos are embedded from the publisher.
Comments
- Tried something like this? Share how it went for you.