Agents gone wrong
A Claude triage bot open to any GitHub user led to an unauthorized Cline CLI release on npm
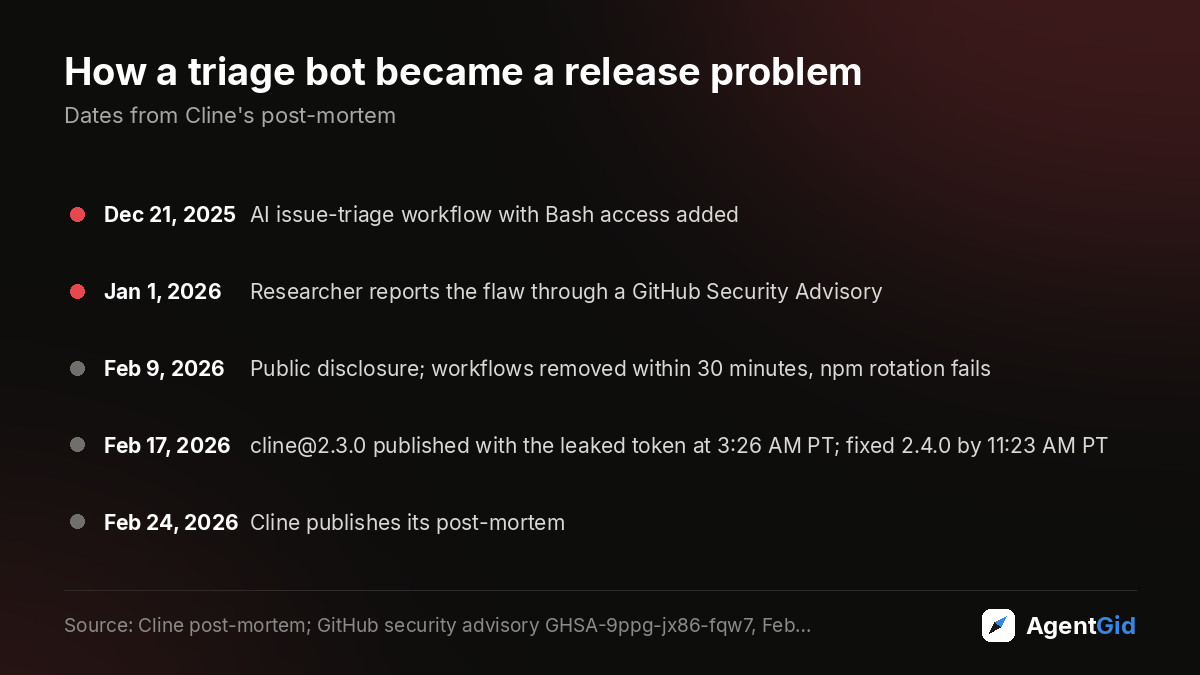
Cline ran claude-code-action with shell access to sort incoming GitHub issues. A prompt-injection flaw in that bot gave a path to Cline's publishing secrets, and on February 17, 2026 someone used a leaked npm token to ship cline@2.3.0.
What the agent did
- The triage workflow let any GitHub user open an issue that Claude read with Bash access, so a crafted issue title could run code on the CI runner
- That workflow shared a cache with the nightly release job; flooding the cache past 10 GB and planting entries could reach the release secrets
- A researcher reported it on January 1, 2026; it sat until his public post on February 9, then the workflows were pulled within 30 minutes
- The npm token rotation missed: the wrong token was deleted, and on February 17 the live one was used to publish cline@2.3.0
- The bad release only added a postinstall that installed openclaw globally; 2.4.0 replaced it and 2.3.0 was deprecated by 11:30 AM PT
What it means for you
- Do not give a CI agent that reads issues, PR titles or comments from strangers a shell, write tokens or secrets. Keep it read-only, or require a maintainer label before it runs.
- Keep AI workflows away from release workflows: separate caches, no shared secrets, and short-lived OIDC publishing instead of long-lived npm tokens.
- After rotating a credential, test that the old one is actually revoked rather than trusting a dashboard. That check failed here.
Why it matters
No single step was new: prompt injection, cache poisoning and a missed token rotation. The AI triage bot is what joined them, turning an issue form into code execution next to release secrets. Cline's own conclusion: an LLM with a shell in CI that reads untrusted input is the same as giving every GitHub user a shell.
Impact is as reported by Cline: the payload was a benign package and only the npm CLI was affected, so the lesson is the chain, not the damage.
Source: Cline post-mortem; GitHub security advisory GHSA-9ppg-jx86-fqw7
Every number on this page comes from the source. Our charts redraw those numbers; videos are embedded from the publisher.
Comments
- Tried something like this? Share how it went for you.
Agents in this story
| # | Agent | Gid Score | Downloads 7d | 7d | 30d | Stars | Latest release | ||||
|---|---|---|---|---|---|---|---|---|---|---|---|
| 23 |
ClineCline Bot Inc. |
58 | 105K | up 25.8% | up 10.5% | 71.1K+52/day | 4.1.266d ago | ||||
| 2 |
|
83 | 12.1M | down 4.6% | down 12.5% | 154K+137/day | 2.1.316yesterday | ||||
| 6 |
OpenClawOpenClaw Foundation (nonprofit); created by Peter Steinberger |
76 | 3.4M | up 8.0% | up 7.4% | 394K+149/day | 2026.9.363d ago | ||||
| No agents match that filter. | |||||||||||


More agents in action
 Agents gone wrongA Cursor agent wiped PocketOS's production database in 9 seconds with one API call
 Agents gone wrongOne PR title was enough: 4,714 GitHub workflows with AI agents could be hijacked to leak secrets
 Agents in actionWorldwide Express agents close 10,000 freight billing exceptions a week and cut the backlog 75%